IT audit & technology risk

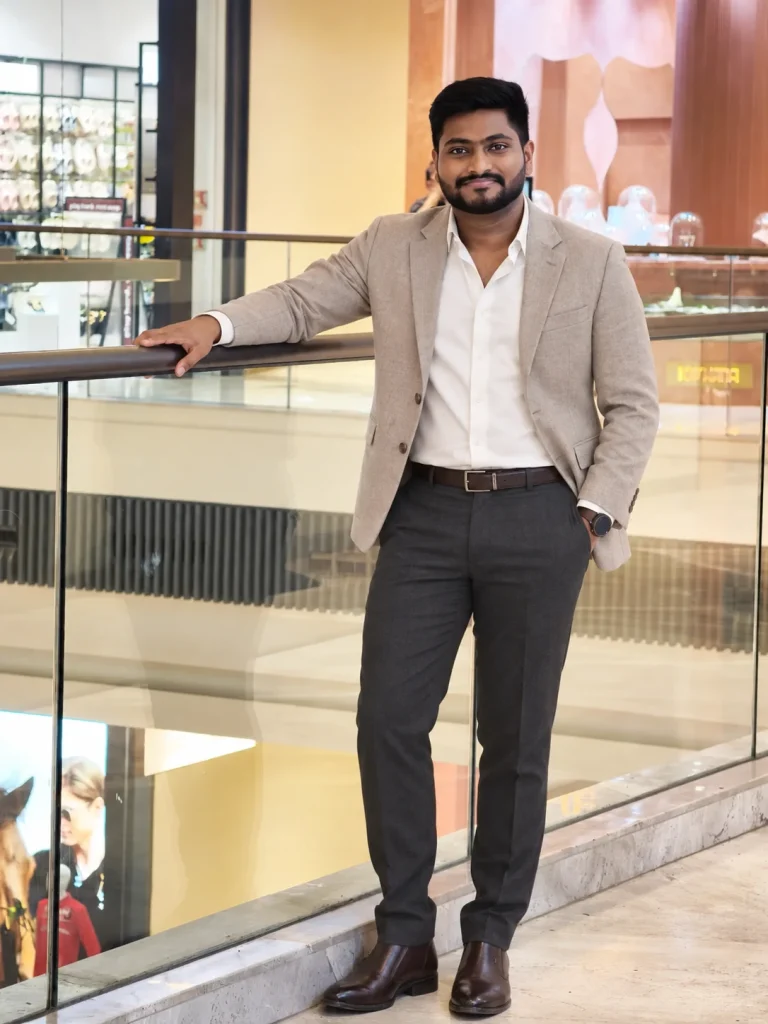
Full-length portrait of Shaswat Manoj Jha

I’m Shaswat, a CISA and Senior Consultant at EY. I lead IT controls reviews, assess how organisations govern AI, and write scripts that cut down manual audit work. See selected work →
Full-length portrait of Shaswat Manoj Jha

Selected work

View all work

A Python script matched HR termination records to directory and application accounts, cutting manual reconciliation effort by about 70%.

EY
Senior ConsultantDigital Risk & IS Audit · since August 2024

About me

I started with programming. These days I spend more time testing IT controls, but I still reach for a script when a check keeps repeating.

At EY, I work in IS Audit & Risk. Before that, I worked at Protiviti and Nangia & Co LLP. My work has covered IT controls, cloud security and data privacy for financial services and insurance organisations.

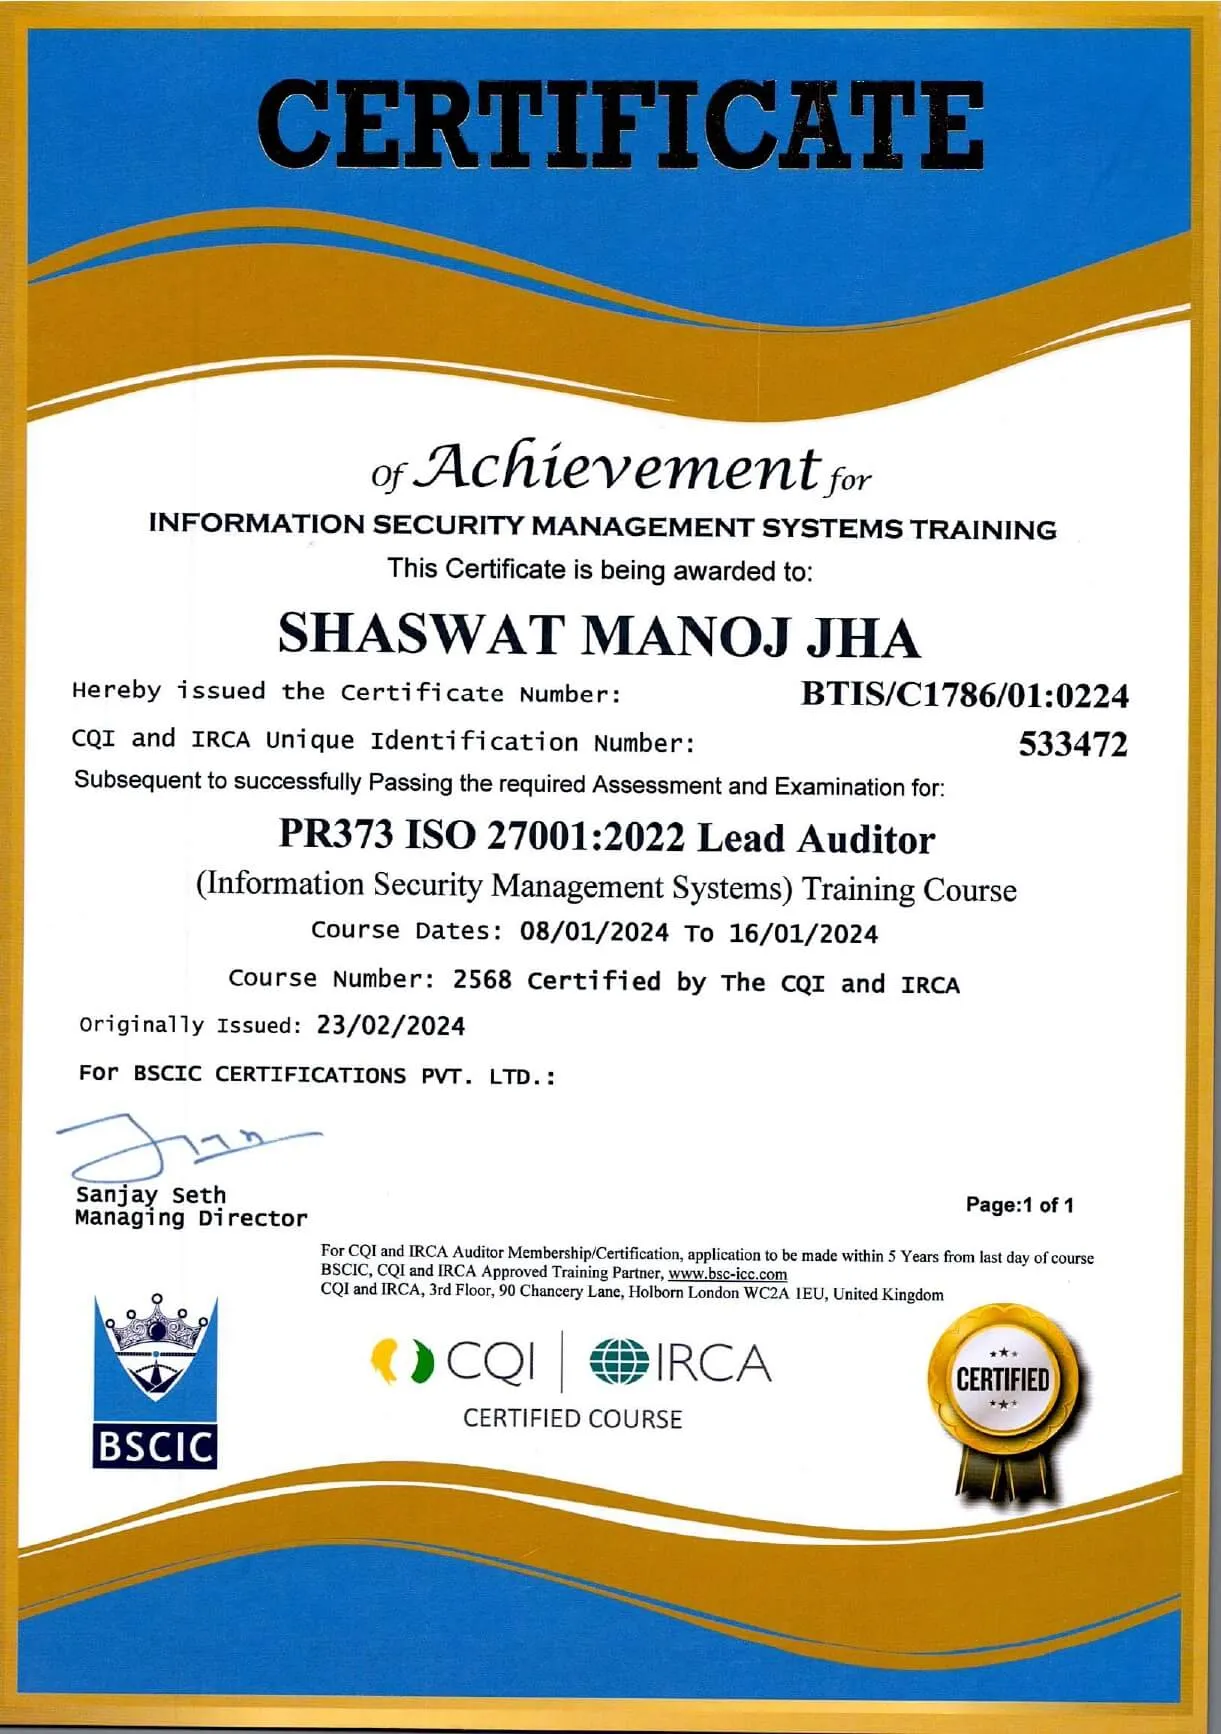
I’m a CISA and have completed lead auditor training for ISO/IEC 27001 and ISO/IEC 42001. I run walkthroughs, test controls and write up the evidence so another reviewer can follow my findings.

I’ve built scripts to flag personal data and match directory accounts to HR departure records. I’ve also responsibly reported an access control flaw in a SaaS platform. See how I approached the projects.

  • I review access management, change management, IT operations and backup and recovery controls. This includes testing both control design and operating effectiveness.
  • For integrated audits, I map IT controls to business processes and document walkthroughs, risk and control matrices, samples and testing evidence.
  • I assess cloud configurations against CIS Benchmarks, including access, encryption, network segmentation and recovery. I also review RPA bot accounts, credential storage and segregation of duties.
  • My recent work includes GitHub access and repository controls, as well as governance over integrated AI tools.
  • I review ISMS policies and carry out gap assessments against frameworks such as ISO/IEC 27001 and NIST SP 800-53.
  • I test interfaces, input checks, master data and report integrity to assess whether applications process data accurately and completely.
  • I review maker-checker workflows, audit trails, access restrictions and configuration settings for risks of unauthorised changes.
  • I recommend improvements to system configurations and the software development lifecycle where testing shows gaps or unnecessary manual work.
  • I map security controls to ISO/IEC 27001, NIST CSF and NIST SP 800-53, and review coverage against IRDAI and RBI requirements.
  • I have carried out SAMA Cybersecurity Framework gap assessments and tracked the resulting findings and corrective actions.
  • For privacy reviews, I check how personal data appears in applications, APIs, logs and reports, including assessments against the DPDP Act 2023.
  • I review business continuity and disaster recovery plans, recovery objectives, backup tests and drill records.
  • I turn policy requirements into testing checklists and evidence requests so that adherence can be assessed.
  • I assess vendor controls for logical and physical access, data protection, service agreements and incident reporting.
  • During on-site reviews, I check data handling, endpoint DLP and how access is granted and removed. I document gaps and follow up on corrective actions.
  • I use Microsoft Visio to map how sensitive data moves between users, processes and systems, then review where it could be exposed.
  • I assess endpoint security and DLP rules, including device controls and restrictions on copying, printing and data transfers.
  • I review asset inventories, patching and EDR coverage, and use dashboards to track gaps and exceptions.
  • I have used Burp Suite, OWASP ZAP and SQLMap for manual and automated testing of web applications.
  • My testing has covered SQL injection, XSS, IDOR, authentication and access control flaws, and security misconfigurations. I record proofs of concept and risk ratings.
  • I work with IT teams to retest fixes and check controls such as least privilege, input validation and rate limiting.
  • I prepare audit scopes, methodologies, effort estimates and acceptance criteria for proposals.
  • I document risk and control matrices, workpapers and supporting evidence so that another reviewer can follow the testing and conclusions.
  • I use Power BI and presentation reports to explain findings, their risk and the actions needed to address them.

Experience

Tools I use

Audit & GRC

AuditBoard
RSA Archer
TeamMate+

Identity & access

Active Directory
Microsoft Entra ID
SailPoint
CyberArk PAM

Cloud security

AWS
Microsoft Azure

Data protection & monitoring

Forcepoint DLP
Splunk

IT service management

ServiceNow
Jira

AI tools reviewed

GitHub Copilot
Microsoft 365 Copilot

Enterprise applications & file transfer

Oracle ERP
SAP SuccessFactors
Axway SecureTransport MFT

Automation, reporting & documentation

Python
SQL
Power BI
Microsoft Visio
Microsoft Office

Security testing

Burp Suite
OWASP ZAP
Kali Linux
Metasploit

Education

MBA – Information Technology and Financial Management
2022 - 2024
Swami Vivekananda Subharti University, Meerut (Distance)
B. Tech – Computer Science and Engineering (81%)
2018 - 2022
Madhyanchal Professional University, Bhopal (Full-Time)

Get in touch

    Fields marked * are required.