ISO/IEC 27001:2022 Lead Auditor – Information Security Management Systems (ISMS)
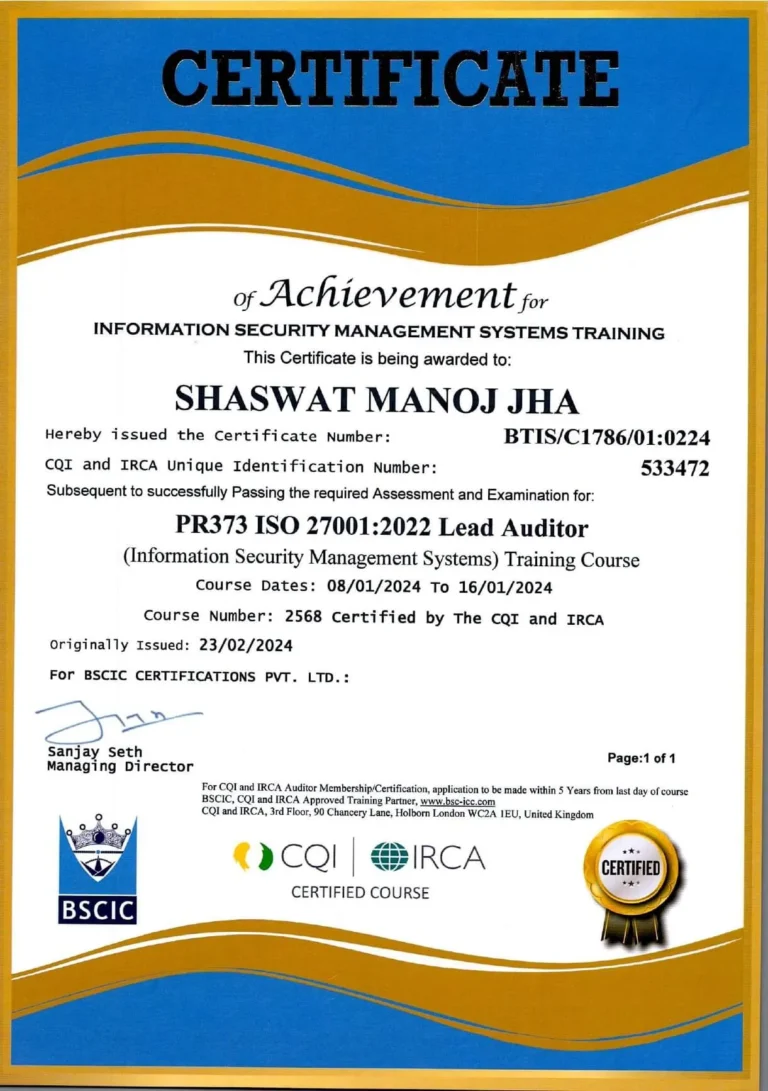
I completed ISO/IEC 27001:2022 lead auditor training in January 2024 and received the certificate in February. The training covered audits of an Information Security Management System (ISMS), including planning, evidence collection, reporting and follow-up.
The exercises focused on assessing an organisation’s security management system against the standard and documenting non-conformities.
Category
Information
Security
Issued By
CQI – IRCA
Issue Date
23 Feb 2024
Training Dates
08.01.24 – 16.01.24
Certificate ID
BTIS/C1786/01:0224
CQI-IRCA ID
533472
Curriculum
The training included simulated audit exercises covering:
- The structure of ISO/IEC 27001:2022 and an ISMS.
- Organisational context, leadership and risk planning.
- Information security risk assessment, treatment and control selection.
- Audit scope, objectives, schedules and preparation.
- Interviews, sampling and collection of audit evidence.
- Writing findings and reviewing corrective actions.
- Audit team roles, ethics and impartiality.
- Closing an audit and following up.
What I learned
I practised planning an ISMS audit, collecting evidence and writing findings. I also studied Annex A controls, their relationship to security risks, and how to assess corrective actions after an audit.
This training is relevant to my policy reviews and security assessments. It provides a reference for checking how an ISMS is documented, operated and reviewed.