Ethical Hacking Training
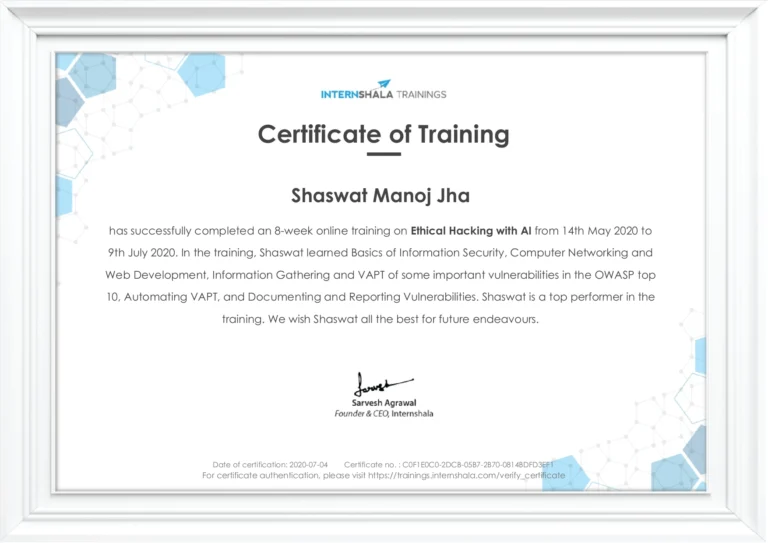
I completed Internshala’s eight-week Ethical Hacking training in 2020, with a final score of 100% and a Top Performer recognition. The course included a virtual lab, 72 challenges and a final web application assessment.
For the final project, I tested a simulated eCommerce site and wrote a vulnerability assessment and penetration testing report.

Category
Cybersecurity
Issued By
Internshala Trainings
Course Duration
8 Weeks
Training Date
May 14, 2020 – July 9, 2020
Marks Obtained
100% (Top Performer)
Verification Links
Course Curriculum
- Information security and networking basics.
- Information gathering and web technologies.
- Web VAPT, OWASP and SQL injection.
- IDOR, rate limiting, file uploads and business logic flaws.
- XSS, CSRF and client-side vulnerabilities.
- Security misconfigurations and vulnerable frameworks.
- Testing automation and secure coding.
- Documenting findings and writing a VAPT report.
The virtual lab included 72 challenges and one final project.
What I learned
I practised the steps of a web application assessment: gathering information, testing, validating a finding and writing it up. The lab gave me examples of both client and server-side vulnerabilities.
Final project: eCommerce application assessment
I assessed a simulated eCommerce site in the training lab. I found issues including SQL injection, IDOR and XSS, and documented them with risk ratings and recommended fixes.
The tools included Burp Suite, OWASP ZAP, SQLMap, Nmap and DirBuster, along with Python scripts. I submitted a 126-page VAPT report and received 100% for the project.
Project Report
This project gave me practice with both testing and reporting. The report was as much a part of the work as finding the vulnerabilities: I had to explain what I found and how it could be addressed.